Everyone assumed Google’s new sideloading rules meant a blanket switch flipped across every phone in four countries at once.
A clarification Google posted the day before enforcement began says otherwise, and after reading the fine print, I think it matters more than the original announcement did.
What exactly changed with this rollout?
The original read suggested a blanket operating-system checkpoint that would block sideloads on every device in a pilot country. Google’s revised wording says enforcement runs through participating stores, the distribution channels themselves, and only on certified Android devices, phones built and licensed to run Google’s own app suite.
A custom ROM or uncertified build isn’t automatically included, at least not yet. I’ve seen enough Android rollout clarifications to know the wording matters. Targeting storefronts first gets Google compliance from major marketplaces without instantly breaking standalone APK installs elsewhere.
Verified apps still install instantly, no matter which store they came from.
How does the 24-hour delay work?
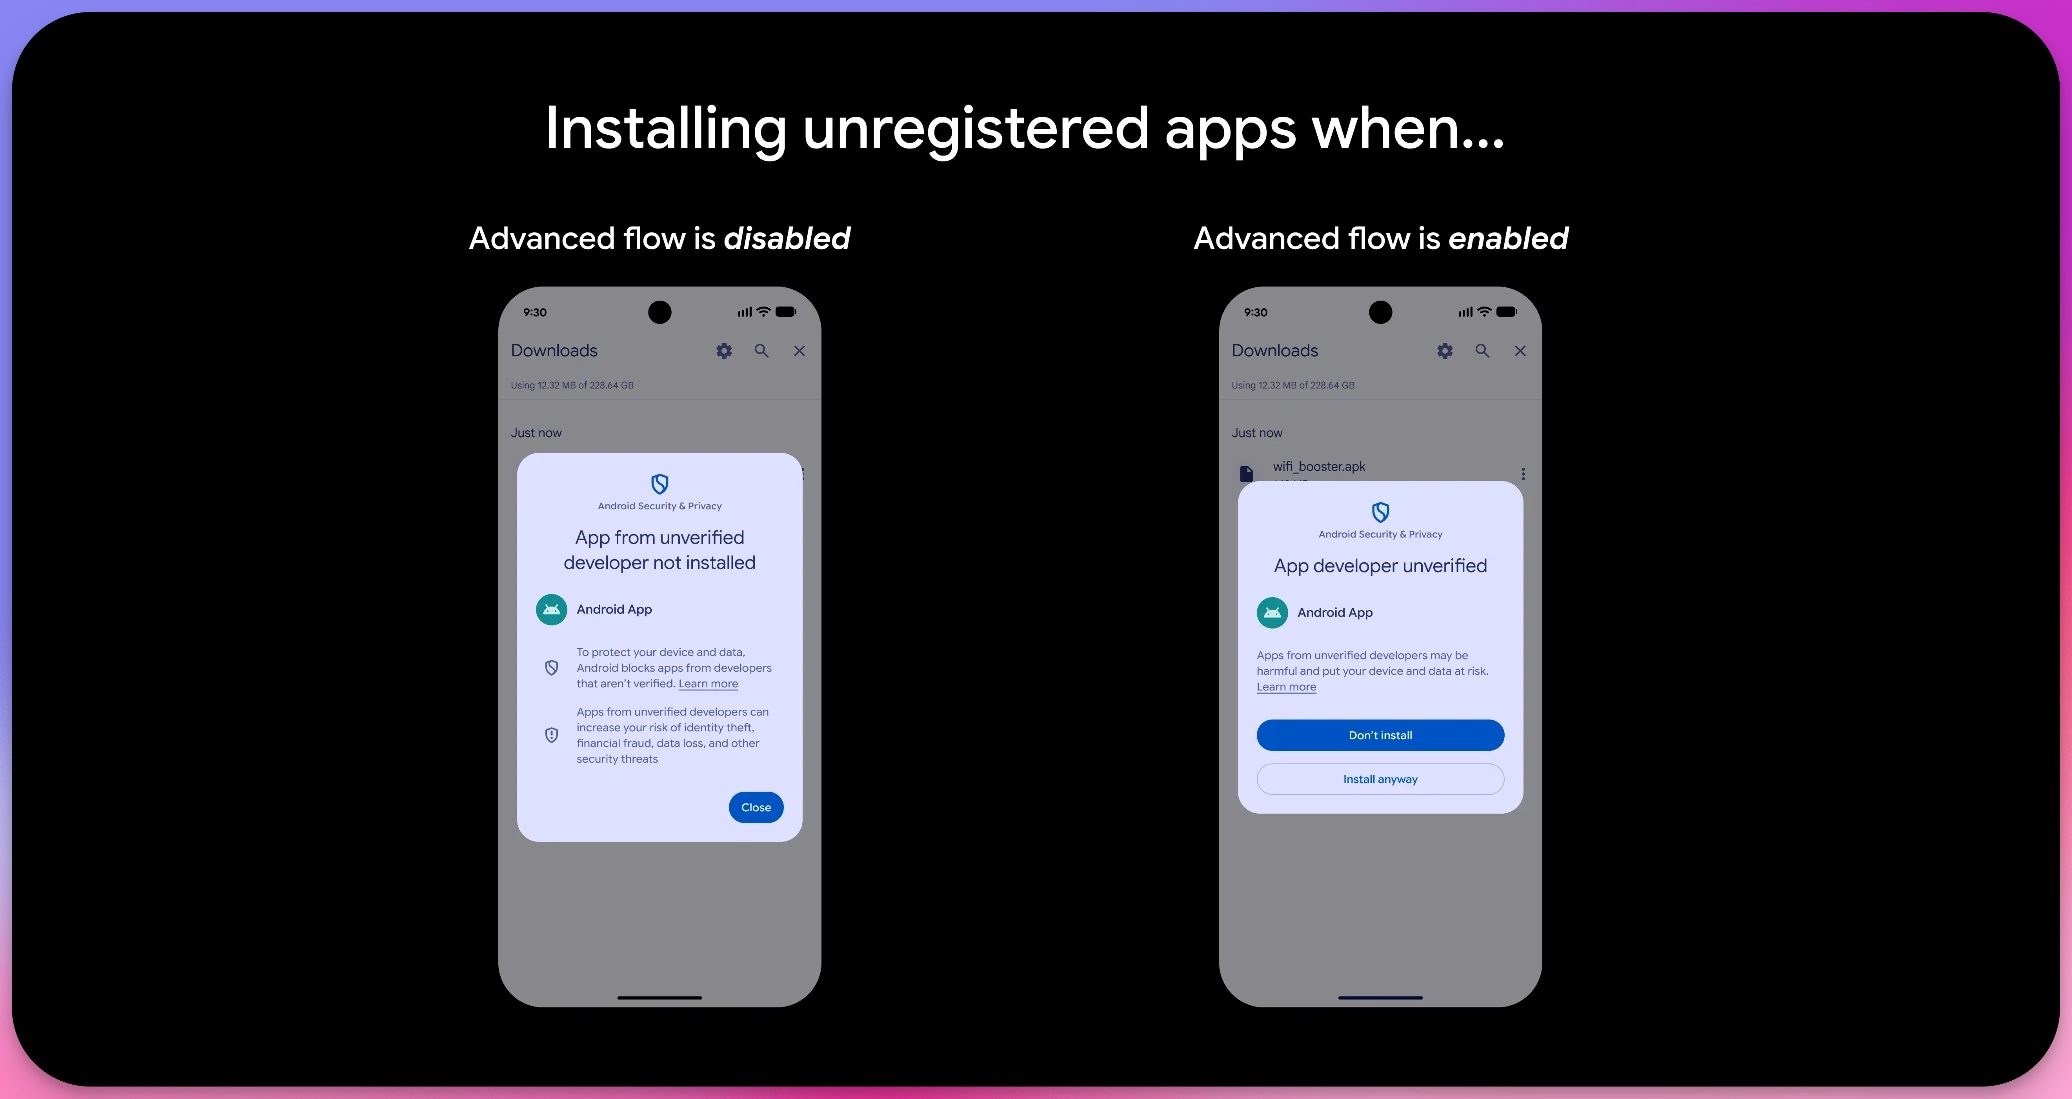
Anything from an unregistered developer trips Android Developer Verifier, a new background check that routes the install through a rather tedious Advanced Flow: a Developer Options toggle, a device restart, then a mandatory 24-hour wait.
However, this is a one-time, device-level delay to unlock the unverified installation setting. Once the 24 hours pass, you can leave the permission enabled for seven days or indefinitely, meaning you don’t face a delay for every single app. Installing over ADB, a direct command-line connection, skips that wait entirely for developers and power users.
What stands out to me is where Google has placed the friction: the real pressure lands on storefronts like Samsung’s Galaxy Store, Xiaomi’s GetApps, and the other authorized marketplaces, which now need every listed developer verified.
Google first floated this 24-hour wait back in spring, well before developer verification itself began rolling out to Play Console accounts. Now that I’ve seen the rollout wording in practice, the distinction is clearer. It’s now enforced in four countries starting September 30, with a full global rollout still committed for sometime in 2027.
RELATED COVERAGE:
- Android 17 just got a security upgrade you’ll want to turn on
- Refer a friend to a Pixel phone, and you could earn up to $500 in Google Store credit
- Opera’s Android browser now keeps you connected abroad with a built-in travel eSIM
- File-notification systems can expose your activity across popular operating systems, even when attackers can’t access your files