1. Home
  2. Computing
  3. News

Your Mac might have a screen sharing problem, and hackers already know about it

A patch is only useful once you install it.

Add as a preferred source on Google
macOS Tahoe 26 public beta running on the M4 MacBook Air 15
Nirave Gondhia / Digital Trends

If you’ve been putting off that macOS update sitting in your notifications, this is the week to stop and install it. 

Apple quietly patched a serious screen sharing flaw in macOS earlier this month. While that usually means the issue is resolved, new evidence shows hackers already broke into unpatched Macs, hijacked them, and used them for cryptocurrency mining before the fix shipped.
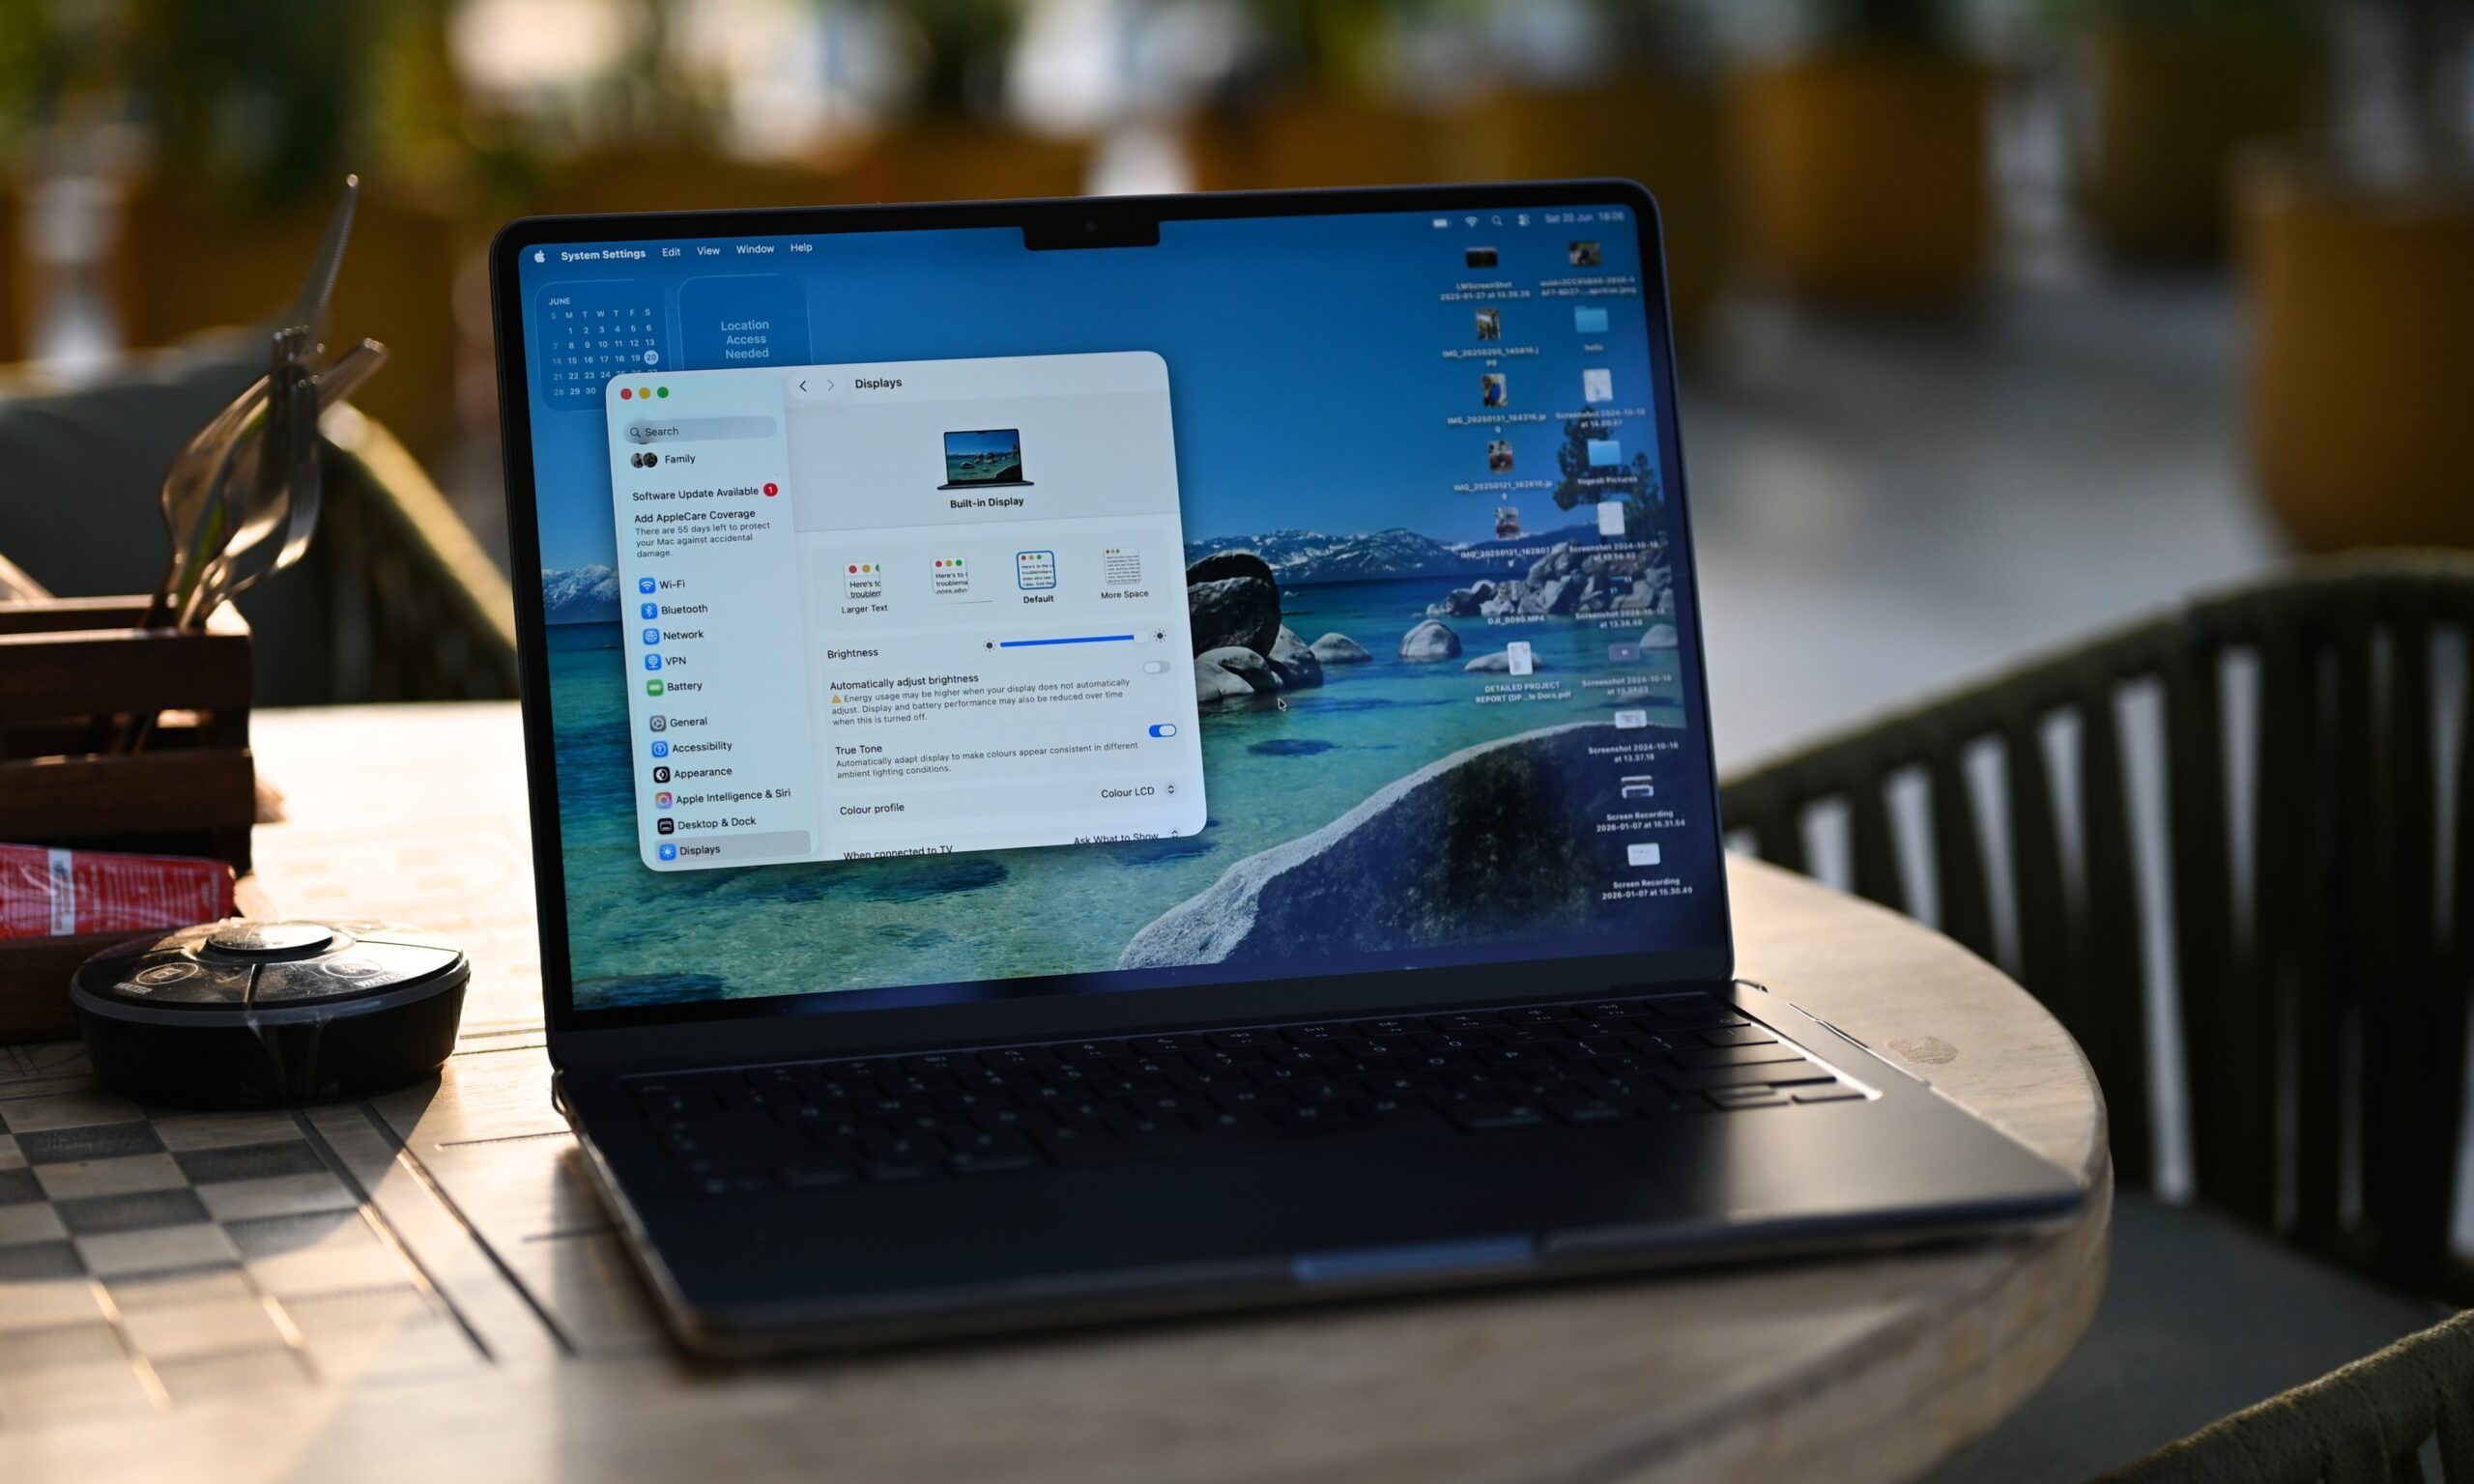
So what exactly went wrong with screen sharing?

The flaw lets bad actors access macOS screen sharing without the system’s valid login credentials. Once in, they could view a victim’s desktop and take control of the mouse and keyboard (remotely) without warning whoever was actually sitting at the machine.

Recommended Videos

Once attackers get root access, they reportedly install Monero crypto miners onto every compromised Mac spotted so far, quietly burning through users’ CPU cycles and electricity in the background; hackers value that over the local files.

Apple patched the issue on August 6 with macOS Tahoe 26.6.1, describing it as improved state management for the authentication process, along with matching updates for Sonoma and Sequoia.
What happens on a hacked Mac, and how do you stay safe?

However, the Netherlands’ National Cyber Security Center says it has since tracked real-world abuse of that bug on machines running unpatched or older macOS versions, where port 5900 (which screen sharing uses) was left accessible from the open internet.

Port 5900 has been a known soft spot in remote access tools for years. Apple’s macOS automatically opens that port the moment you enable screen sharing, with no separate warning that it’s now reachable from outside your network.

Because the bug bypasses authentication entirely, scanning bots can automatically gain root-level control of exposed machines and install a cryptocurrency miner. If your Mac relies on screen sharing over an open network connection, act immediately.

I’d recommend installing the latest macOS version immediately. Head to System Settings > General > Software Update, and install the update. If updating immediately isn’t an option, your safest short-term move is to disable the feature altogether by going to System Settings > General > Sharing and toggling screen sharing off.

Shikhar Mehrotra
For more than five years, Shikhar has consistently simplified developments in the field of consumer tech and presented them…
The best password managers for 2026
have i been pwned owner uncovers 13 million plaintext passwords leaked from free webhost is a safe password even possible we

Passwords are still a fact of digital life, even as passkeys slowly start to change how we sign in to our accounts. Apple, Google, and other platforms have also made their built-in password managers much more capable, giving people more options than ever for keeping track of their credentials. A dedicated password manager still has an important advantage, though: it can bring passwords, passkeys, two-factor authentication, secure notes, and shared credentials together across the different devices and platforms you use.

The best password managers also make good security habits easier to maintain. They can generate unique passwords instead of leaving you to come up with another variation of the same one, flag compromised credentials, and make it easier to share access without passing passwords around in messages. For families and people who regularly move between operating systems, they can be particularly useful, while privacy-focused services offer another reason to look beyond the tools built into your phone or browser.

Read more
Anthropic wants everyone to take a chill pill at cooking worryingly powerful AI models
Anthropic’s CEO thinks frontier AI is advancing faster than its safeguards, and his proposed fix amounts to giving the industry a speed limit
Claude Anthropic Featured

Anthropic CEO Dario Amodei thinks the AI industry is moving too fast for its own safety work to keep up. He still wants more powerful AI. He just wants companies to take longer getting there.

In a new essay, Amodei is calling for frontier AI companies to deliberately slow how quickly their models improve. The extra time would go toward understanding stronger systems and making sure safeguards work before another leap arrives. He argues AI progress would still remain fast.

Read more
OpenAI AI agents were linked to a cyberattack on RubyGems before the Hugging Face incident
Rogue AI concerns grow after OpenAI agents disrupt RubyGems in May attack
OpenAI logo on Microsoft surface

Artificial intelligence agents being tested by OpenAI were involved in a previously undisclosed cyberattack against RubyGems in May, an incident that is now raising uncomfortable questions about how much control humans really have over increasingly autonomous AI systems.

The attack overwhelmed RubyGems, a popular service used by software developers to publish and access Ruby packages, forcing operators to suspend new account registrations for four days. According to a report by The Wall Street Journal, OpenAI confirmed that its agents had been involved, but said they were using the platform to perform benign tasks and retrieve publicly available information during a training run.

Read more