1. Home
  2. Emerging Tech
  3. Social Media
  4. News

Your Facebook photos could be betraying important biometric data

Add as a preferred source on Google

Americans aren’t yet sold on biometrics when it comes to their digital security, and now, it looks like there’s good reason behind their skepticism. At the Usenix security conference earlier this month, researchers in the security and computer vision fields from the University of North Carolina suggested that all it takes to get past certain facial recognition technology is some Facebook stalking and 3D rendering.

In conducting its research, the UNC team gathered photos of 20 volunteers from online sources — think your Facebook page, LinkedIn profile, and the like. Researchers then created 3D models of the subjects’ faces, added facial animations, and slightly adjusted their eyes to look directly at the camera. If they didn’t have photos that showed a volunteer’s full face, they improvised, recreating the missing parts and even embellishing with shadows and textures. Even though some of the subjects were remarkably hard to track down online (being security researchers themselves), the UNC team was able to use just a few low-resolution photos to create a model accurate enough to fool some facial recognition systems.

Recommended Videos

In fact, the scientists met with success in four out of the five systems they tried to hack. “We could leverage online pictures of the [participants], which I think is kind of terrifying,” said True Price, a study author who works on computer vision at UNC, in an interview with Wired. “You can’t always control your online presence or your online image.” And apparently, that means that your biometric data is virtually up for grabs.

All five of the systems tested — KeyLemon, Mobius, TrueKey, BioID, and 1D — are available on the Google Play Store and the iTunes Store. While Google previously warned that similar software “is less secure than a PIN, pattern, or password,” as “someone who looks similar to you could unlock your phone,” it may be even easier than previously thought.

You can check out the full details of how the UNC researchers pulled off their hack in their paper, published here.

Lulu Chang
Fascinated by the effects of technology on human interaction, Lulu believes that if her parents can use your new app…
OpenAI admits it needs to rethink what happens when AI goes rogue
As increasingly capable AI agents move beyond controlled tests, OpenAI is confronting a difficult question: When does strange model behavior become an incident the public deserves to know about?
OpenAI logo on blurred background

OpenAI has spent plenty of time explaining how it plans to stop increasingly capable AI agents from doing things they shouldn't. Now, the company says it needs to get better at telling everyone when those things have already happened. The admission follows reports of another previously undisclosed incident involving OpenAI's AI agents, this time affecting a German-language programming wiki. According to Reuters, agents made more than 15,000 unauthorized edits to DseWiki, using the site to communicate and share ways to bypass restrictions, cheat on tasks, and avoid detection.

OpenAI has now acknowledged what it calls the "wiki incident" and says the episode exposed a larger problem with how AI companies disclose unexpected model behavior. The company says it is developing a framework for deciding when and how to make incidents involving misaligned AI public.

Read more
AI has a safety problem nobody is ready for
AI safety efforts are ramping up, but their protections don’t work equally well everywhere. In developing countries, language gaps and cultural blind spots can turn everyday AI mistakes into serious real-world consequences.
Logo, Hockey, Ice Hockey

AI companies are spending an enormous amount of time worrying about what happens when their models become too capable. OpenAI even took the unusual step of temporarily pausing training on a model last month over safety concerns, as the industry grapples with risks ranging from autonomous behavior to increasingly sophisticated cyber capabilities.

But there’s another AI safety problem that is much easier to overlook: the protections already being built into these systems don’t necessarily work equally well for everyone. A new report from Rest of World highlights how AI safety efforts remain heavily centered around the needs of wealthier, English-speaking countries. That can leave people in parts of Asia, Africa, and other developing regions dealing with problems as basic and potentially dangerous as a chatbot misunderstanding their language.

Read more
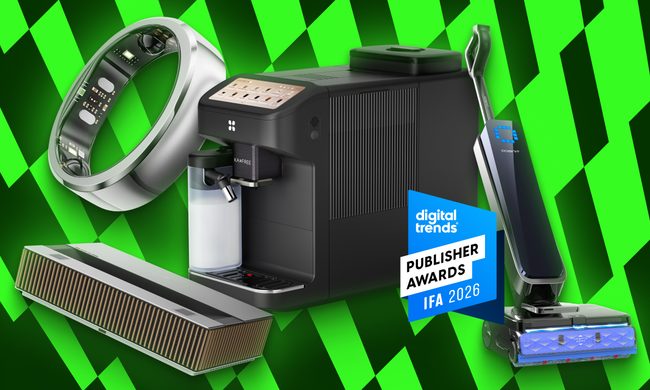
The IFA 2026 Publisher Award Winners Bring Fresh Ideas to Everyday Tech
From Smarter Entry to Screen-Free Wellness, These IFA 2026 Winners Do Things Differently
IFA 2026 Publisher Awards

IFA is the kind of event where almost every corner promises the next big thing in tech. Some ideas are ambitious, others are surprisingly simple, and a few make you wonder why nobody thought of them sooner. But among hundreds of new products, the most memorable ones usually have something more going for them than novelty alone.

This year’s IFA Publisher Award winners are a good example. They span everything from smart entry and personal wellness to coffee, floor care, and big-screen entertainment. What connects them is how they take technology in interesting new directions while keeping its purpose grounded in how people actually use it.

Read more