  1. Home
  2. Computing
  3. News

Hackers wiped out this popular tax prep software as filing deadline looms

Add as a preferred source on Google

The IRS-authorized tax preparation software service eFile.com recently suffered a JavaScript malware attack in the middle of tax season, according to BleepingComputer.

The nefarious JavaScript file has been identified as popper.js and has been observed by eFile.com users as well as by security researchers. The malware is believed to have surfaced on the service around mid-March and has interacted with “almost every page of eFile.com, at least up until April 1st,” the publication added.
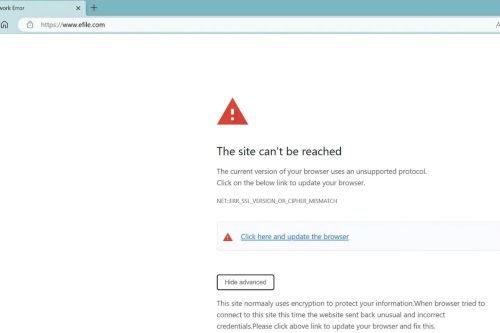
SSL error shown by eFile.com (u/SaltyPotter on Reddit).
Image used with permission by copyright holder

Encountering this infected JavaScript on eFile.com would likely result in seeing a broken link, which is returned by infoamanewonliag[.]online. Users of the service began discussing the possibility of an attack on Reddit on March 17, noting that an SSL error message they were receiving appeared to be fake.

Recommended Videos

Researchers confirmed that the errors were indicative of a malware attack, also connecting them to the JavaScript malware file update.js. This file acted in the malware as the cue to make users download the file, and can ultimately vary depending on the browser being used, such as [update.exe – VirusTotal] for Chrome or [installer.exe – VirusTotal] for Firefox.

Having conducted its own research on the malware, BleepingComputer learned that the bad actors orchestrating the malware did so from a Tokyo-based IP address, 47.245.6.91 that was likely hosted with Alibaba. The publication also connected the IP address to the infoamanewonliag[.]online domain, which is also associated with the attacks.

BleepingComputer was able to study a sample of the malware script that was uncovered by the Security research group, MalwareHunterTeam, which was written in PHP. The publication determined that the script is a “backdoor malware” that lets hackers control infected devices remotely. Once infected, the PHP script runs in the background, allowing the malware to connect to a device from a control server every ten seconds to perform whatever nefarious actions the bad actor wants.

Despite the malware being a “basic backdoor,” there is a lot of potential for bad actors to use it for very bad purposes including stealing credentials, or stealing data for extortion, the publication noted.

MalwareHunterTeam criticized eFile.com for not addressing the attack for several weeks. It has since been resolved; however, the extent of its impact remains unknown.

Fionna Agomuoh
Fionna Agomuoh is a Computing Writer at Digital Trends. She covers a range of topics in the computing space, including…
Three hikers trusted Gemini to plan a hike and had to be rescued the next day
Rescuers say Gemini advised the group to carry far less food and water than they needed.
Mount Shasta, United States

AI chatbots can help plan a vacation or suggest what to pack. But there are situations where advice from someone who actually knows what they are doing is the safer choice.

As reported by the Chicago Tribune, three novice hikers from Roseville, California, had to be rescued from Mount Shasta after becoming stranded overnight. According to the Siskiyou County Sheriff’s Office, they had used Google Gemini to help plan the climb. The sheriff’s office said Gemini advised the group to carry far less food and water than they needed.

Read more
Windows 11 is about to turn on a setting that could hurt gaming performance
Microsoft will start enabling Memory Integrity on more Windows 11 PCs in October
A gaming PC with RGB synced lights running Apex Legends.

Microsoft is preparing to enable Memory Integrity on more Windows 11 PCs starting in October. The security feature is meant to protect systems from malicious code, but there is one reason gamers may want to keep an eye on it.

Microsoft has previously acknowledged that Memory Integrity can affect gaming performance on some Windows 11 systems. Back in 2022, the company even published instructions explaining how gamers could temporarily disable Memory Integrity and Virtual Machine Platform if they were causing problems.

Read more
AI chatbots will agree and misinform if you just put a little pressure, warns research
ChatGPT 3.5 proved the most vulnerable when false claims were repeated over and over
Claude AI on an iPhone.

AI chatbots have a well-documented habit of hallucinating information and sometimes agreeing with users even when they are wrong. A new study suggests that simply refusing to take no for an answer can make the problem worse.

Researchers from the University of Arizona tested seven AI models, including GPT-3.5, GPT-4o, GPT-4o-mini, Claude 3.5 Sonnet, Gemini 1.5 Pro, Llama 3 70B, and DeepSeek-R1. Instead of judging them from a single response, researchers kept conversations going while repeatedly feeding the models information they knew was false.

Read more