  1. Home
  2. Computing
  3. News

Elon Musk’s Starlink satellites hacked by $25 homemade device

Add as a preferred source on Google

A $25 hacking tool that can seemingly breach Starlink’s internet terminals has been revealed by a security researcher.

As reported by Wired and Gizmodo, Lennert Wouters, who works at Belgian university KU Leuven, showcased how to infiltrate the satellite dishes at the Black Hat Security Conference.
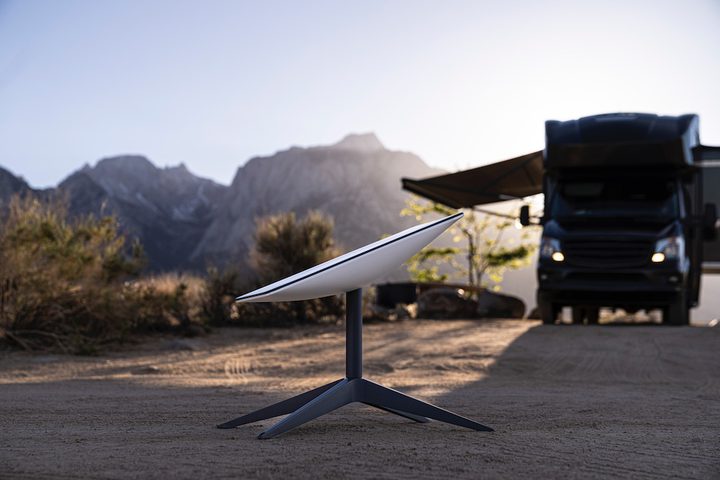
A Starlink dish next to an RV.
SpaceX

For reference, Starlink was started by Elon Musk with the aim of providing internet connections around the world. By launching 3,000 satellites into orbit, the company has attracted over 500,000 subscribers.

Recommended Videos

However, Wouters has now found a way to hack into the dishes due to various hardware vulnerabilities. If left exposed, this would give threat actors free rein to access Starlink’s system and then run custom code on the network’s devices.

In order to find any exploits within the satellite dish’s software, Wouters purchased a dish and attached his hacking device onto it. The tool itself was formed via a custom circuit board (modchip), with the price of the overall parts required for the device costing just $25.

The homemade printed circuit board (PCB) is then capable of shorting the system, albeit temporarily, via a fault injection attack — this method, or glitch, was used to circumvent the security measures Starlink has in place.

After revealing the hack at his presentation, Wouters released the tool on GitHub, which gives a breakdown on how to perform the attack itself.

Starlink was made aware of the security defects last year by Wouters himself, and even paid the researcher for his efforts via its bug bounty scheme.

Even though parent company SpaceX patched the vulnerabilities at the time — prompting Wouters to modify the modchip — it seems the core issue cannot be resolved without a new model of the main chip being produced. As such, he stated that every user terminal associated with Starlink is currently exposed.

A public update was confirmed to be in the works by Starlink, but Wouters stressed that the nature of the company’s operations exposes them either way. “The widespread availability of Starlink User Terminals (UT) exposes them to hardware hackers and opens the door for an attacker to freely explore the network,” he said.

“Our attack results in an unfixable compromise of the Starlink [user terminal] and allows us to execute arbitrary code,” he continued. “The ability to obtain root access on the Starlink [user terminal] is a prerequisite to freely explore the Starlink network.”

Wouters also has experience in hacking another product from an Elon Musk company — he’s created hardware that can unlock a Tesla electric vehicle within just 90 seconds.
Zak Islam
Former Contributor
Zak covers the latest news in the technology world, particularly the computing field. A fan of anything pertaining to tech…
What’s next for humanoid robots? Groping and sexual assault, apparently
German police investigate robot over alleged sexual harassment of teenage girl
Humanoid Robot

German authorities have launched an investigation after a robot allegedly touched a 16-year-old girl inappropriately and made sexual gestures on a street in Cologne. Police have seized the robot and the mobile phones of two young men suspected of controlling it, as investigators try to establish whether its movements were programmed in advance or directed in real time.

The incident raises unusual questions about accountability when robots are used to harass people in public. The suspected owner, aged 16, and his 19-year-old companion have not been charged, but police are investigating possible sexual harassment. Authorities say they are unfamiliar with a case of this kind, making it an unusual challenge for law enforcement.

Read more
US banks want to block AI agents from moving your money. Well, at least that’s one good move.
Letting a chatbot handle your finances sounds convenient until someone asks who pays for its mistakes.
ai-agents-on-phone

AI agents want to handle more of your life, including your money, but US banks are drawing a line when these AI assistants try to move funds on your behalf. Charles Schwab and JPMorgan Chase are now restricting outside AI agents from taking financial actions, citing security risks and unanswered questions about who takes responsibility when things go wrong.

Charles Schwab CEO Rick Wurster told Bloomberg that Schwab is actively blocking unauthorized AI agents, including Meta's Muse, from moving client money. JPMorgan Chase CEO Jamie Dimon made a similar call this week, so this isn't just one bank being cautious.

Read more
MapQuest can now show you the cameras keeping an eye on your commute
MapQuest is back, and now it’s exposing who’s watching your neighbourhood
Surveillance cameras

MapQuest has introduced a new surveillance layer that lets users see the reported locations of outdoor surveillance cameras and automated licence plate readers, including those operated by Flock Safety. The feature gives drivers and residents a clearer picture of the surveillance infrastructure around their neighbourhoods, at a time when law enforcement's use of these cameras is under growing scrutiny.

The new layer can be enabled through MapQuest’s Map Options menu, alongside existing options for traffic and incidents. It covers cameras from multiple manufacturers, including Motorola Solutions, Genetec, Axis Communications, Axon, Leonardo, Neology, Rekor, PlateSmart, Ubicquia and Verkada. The company has promoted the feature with the tagline “The Roads Have Eyes!”

Read more