North Korean hackers are attempting to lure in cryptocurrency experts via bogus job offers for crypto exchange platform Coinbase.
As reported by Bleeping Computer, a campaign orchestrated by the well known North Korean Lazarus hacking group has been uncovered, and its target is those involved in the increasingly popular fintech (financial technology) industry.
In what is clearly part of a social engineering attack, the hacking group engages in conversation with targets through LinkedIn, which ultimately culminates in a job offer being presented to the potential victim.
Coinbase is a leading cryptocurrency exchange company, so, at face value, many who are not privy to the attack will naturally be interested in adding them to their resumes. However, if the attack were to succeed, then the consequences could lead to untold amounts of crypto wallets being seized and stolen.
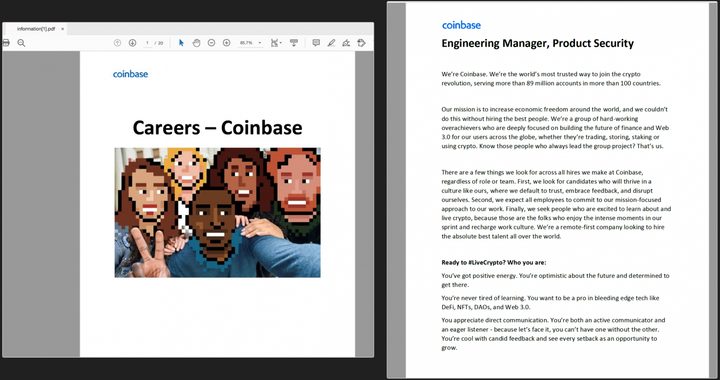
Hossein Jazi, who works as a security researcher at internet security firm Malwarebytes and has been analyzing Lazarus since February 2022, said individuals from the cybergang are masquerading as employees from Coinbase. The scam attracts potential victims by approaching them to fill the role of “Engineering Manager, Product Security.”
If that individual falls for the fake job offer, then they’ll eventually be given instructions to download a PDF explaining the job in full. However, the file itself is actually a malicious executable utilizing a PDF icon to trick people.
The file itself is called “Coinbase_online_careers_2022_07.exe,” which seems innocent enough if you didn’t know any better. But while it opens a fake PDF document created by the threat actors, it also loads malicious DLL codes onto the target’s system.
After it’s successfully deployed onto the system, the malware will then make use of GitHub as a central command center in order to receive commands, after which it has free rein to carry out attacks on devices that have been breached.
U.S. intelligence services have previously issued warnings regarding Lazarus’ activity in issuing cryptocurrency wallets and investment apps infected with trojans, effectively allowing them to steal private keys.
And the group’s efforts have been lucrative, to say the least — the FBI found that it had stolen cryptocurrency with a value of over $617 million at the time.
This particular attack, which is connected to a blockchain-based game, materialized due to another deceptive PDF file, which was sent as a job offer to one of the blockchain’s engineers. Once the file was opened, the individual’s system was infected, subsequently paving the way for Lazarus to locate a security flaw and take advantage of it in a big way.
In any case, the prospect is a scary one: opening a single PDF file leading to the entire network being compromised. In the case of Coinbase, which handles billions of dollars in crypto transactions, one can only imagine what the outcome and financial ramifications would be if Lazarus indeed manages to find a way in.
For the time being, if you’re approached by Coinbase in any capacity, it might be a good idea to be cautious of opening any files.