The infamous Trickbot ransomware botnet is on the rise, according to reports from multiple security research firms.
After being dismantled in a joint effort by Microsoft and the Pentagon, the Russian-speaking group of cybercriminals is spreading its malicious software once again, and security research firms are classifying it as a “critical” threat.
Where does it usually show up? Well, in your inbox, of course — the most vulnerable place on the internet.
What is Trickbot?
Trickbot is a botnet with over a million “zombie” computers. Botnets work by infecting computers with malware to add them to a distributed network of other computers. With the malicious software operating, hackers are able to pool the collective resources of the network to launch ransomware attacks, distributed denial of service attacks, and more.
Trickbot is one of the more infamous examples, operating out of numerous locations in Eastern Europe, including Russia, Ukraine, and Belarus. As reported by The Daily Beast, the hacker group and the botnet after which they’re named is on the rise again.
Computers become infected mainly through phishing emails, which usually accuse the reader of committing some sort of crime. After clicking one of the links in the email, the hackers are able to execute malicious code and infect your computer, potentially stealing login information or banking credentials. The network then lobs ransomware attacks against high-value targets — usually businesses and wealthy individuals — to extort them.
Bitdefender, one of the leading antivirus services available, says that “Trickbot is more active than ever.” In May, Bitdefender’s detection systems started picking up increased signs of the tvncDll module, which is an updated version of the vncDll module that Trickbot has used in the past. Bitdefender says this module is used for monitoring potential targets, suggesting that Trickbot is planning another string of attacks.
Security research firm Fortinet has also identified a new strain of ransomware called Diavol. As is typical of ransomware, Diavol encrypts the files on your computer and holds them for ransom. With everything locked, you’ll only have access to a text document that asks you to download a browser and pay a ransom to restore your files. Typically, the files aren’t restored after the ransom is paid, as the criminals continue to extort your data.
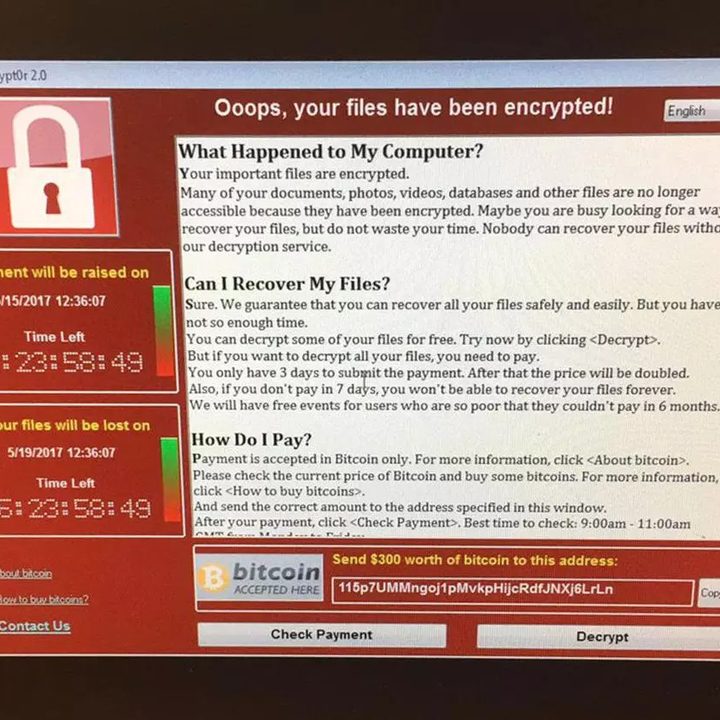
Fortinet identified the new strain as a “critical” threat, and it’s easy to see why. Trickbot was mostly dismantled by Microsoft and the Pentagon prior to the 2020 U.S. election.
Citing fears of interference, Microsoft was able to eliminate about 94% of Trickbot’s critical infrastructure, largely taking the botnet offline. It didn’t get rid of everything, though, and recent reports show that the group has been quick to rebuild.
How to keep yourself safe
Trickbot doesn’t exploit a single vulnerability, so the only way to keep yourself safe is to follow good cybersecurity practices. The most important thing is to regularly update your operating system. Windows updates patch security vulnerabilities and update the list of known threats. If you’re staying on top of Windows updates, you’ll be protected from threats as security researchers are able to identify them.
It’s important to be careful with your email inbox, too. As mentioned, Trickbot is able to spread through malicious links in emails. Usually citing some small crime, the email will ask you to click on a link to pay a fine or to provide proof you didn’t commit the crime. After you click the link, the software is able to infect your machine and potentially spread through your network to other machines.
Although most phishing emails accuse users of committing a crime, that’s not all you have to look out for. We recommend avoiding links from email addresses you don’t recognize altogether. Once you click, there’s no turning back.
If you’re still worried, you can also invest in or at least set up an antivirus program. Windows Defender, which is included for free with Windows, will protect you from most threats. Windows also includes ransomware protection. However, services like Bitdefender and Avira employ behavioral detection systems to identify new forms of malware based on how they act on your machine.