
Just as our everyday lives depend on the Internet, the backbones of nations increasingly rely on the Internet for communication, coordination, and financial transactions. But relying on the Internet also exposes those core functions threats from anywhere in the world. Need examples? Two weeks ago, some 30,000 systems at South Korean banks and broadcasters were wiped out in a coordinated attack – it might have come from North Korea, but investigators are still chasing basic details. Last week, a cyber-brawl apparently between Spamhaus and CyberBunker has caused localized collateral damage and may have shaken some top-tier Internet providers.
Earlier this month, the U.S. Director of National Intelligence James Clapper offered an assessment of current worldwide threats to the United States. The list included terrorism, weapons of mass destruction, competition for dwindling natural resources, and even pandemics. But the first item? Cyber threats.
Why are online threats now the top priority for U.S. national security – the first time they’ve outranked terror networks? And how could the U.S.’s heightened stance impact everyday use of the Internet?
States and governments
The United States loosely categorizes online threats as cyber espionage and cyber attacks. Cyber espionage is about information: things like usernames and passwords but also classified data, intellectual property, and financial details. Cyber attacks, conversely, cause disruption and/or damage. Agents behind both kinds of can vary from so-called “hacktivists” and organized crime to traditional terror networks and – perhaps most significantly – governments.
“State actors continue to top our list of concerns,” said General Keith Alexander, head of the National Security Agency (NSA) and
the U.S. Cyber Command, before the Senate Armed Forces Committee this month.
However, the elevation of cyber threats doesn’t mean the U.S. believes a major cyber attack is imminent.
“We judge that there is a remote chance of a major cyber attack against U.S. critical infrastructure systems during the next two years that would result in long-term, wide-scale disruption of services,” wrote Mr. Clapper. “The level of technical expertise and operational sophistication required for such an attack […] will be out of reach for most actors during this time frame.”
So why the elevated concern? What could a cyber attack do?
One example often offered is the 2003 northeast blackout that disrupted electrical service to an estimated 55 million people in the U.S. and Canada for as long as two days. The outage was famously traced to a single software bug that prevented a beleaguered Ohio utility from spotting a local failure – and things spiraled out of control. It might sound like the plot of a bad movie, but imagine if those events had been triggered by an attacker halfway around the world?
“Our critical infrastructures are all identifiable: they’ve been probed, and they’ve been mapped,” said Frank Cilluffo, Director of the Homeland Security Policy Institute at George Washington University last week in testimony before the House Subcommittee on Cybersecurity, Infrastructure Protection, and Security Technologies. “They have not necessarily been looked at from a computer network attack perspective, but the fact they’ve probed these systems– what other motive could they possibly have? It’s not espionage, it’s to come up with a potential battle plan in the future. Big concern.”
The United States plays this game. Attacking industrial and control software dates back to at least the Reagan era– although it was probably considered counterespionage, not a cyber attack. More recently, the 2010 Stuxnet worm was crafted (probably by the U.S. and Israel) to damage and destroy industrial control systems in Iranian uranium enrichment facilities. The related Duqu worm seemed to be all about gathering intelligence in the Middle East, as was the far more-sophisticated Flame malware detected last year – then killed by its operator.
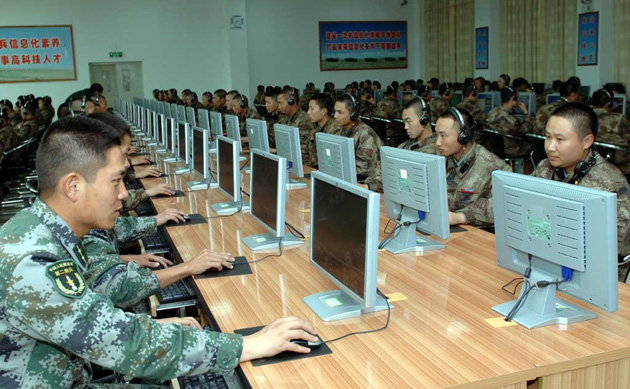
Russia, China, Iran, and North Korea have all been implicated in persistent online espionage and attack activity. Last month security firm Mandiant fingered the Chinese People’s Liberation Army as brazenly running cyber operations out of a 12-story building in Shanghai – alleging this “APT1” unit is one of dozens of hacking outfits run by the Chinese military. Iran is believed to be behind persistent denial-of-service attacks against Bank of America, JPMorgan Chase, Citi, and U.S. government sites during 2011 and 2012, as well as a destructive attack against Saudi Aramco and Qatar’s RasGas last year where malware wiped out more than 30,000 workstations. North Korea seems to be behind major disruptive attacks against South Korea in 2009 and 2011, and maybe this month’s destructive attack against banks and broadcasters.
Follow the money
Where denial-of-service and outright destructive attacks might be a digital form of sabre-rattling for some regimes– or make for great movie plots– cyber espionage is the bread and butter of much state-sponsored online action. Attacking infrastructure could have a rapid ripple effect on an attacking nation – or provoke a forceful response. Stealing information, however, can quietly eliminate strategic, technological, or competitive advantages.
“In the last few years we have shown enough data that proves that the number and complexity of these attacks have been increasing steeply,” said Jamie Blasco, manager of the Vulnerability Research Team at open source security firm AlienVault. “Hundreds, if not thousands, of companies have been already compromised and a huge amount of intellectual property and confidential data has been stolen.”
Mandiant estimated China’s APT1 had stolen “hundreds of terabytes” from more than 140 organizations. Federal agencies, defense contractors, and technology companies are all logical targets of state sponsored cyber espionage, other targets can be surprising.
“Legal firms may be the biggest target of nation states because they have so much proprietary information in their systems,” noted Tim Keanini, chief research officer at enterprise security firm nCircle. “Security isn’t their core competency, and it’s hard to know what needs to be secured. Attackers might be interested in a PDF on a laptop or a Dropbox account, rather than credit card numbers.”
Attackers don’t just target enterprises, businesses, and federal agencies: state agencies get attacked too, and they’re packed with personally identifiable information.
“States collect data from cradle to grave for constituents,” said Chad Grant, senior policy analyst for the National Association of State Chief Information Officers, via email. “If you ask state officials how many attacks they receive, the first response you’ll hear is that they’ve grown exponentially each year. The second thing you’ll hear is that the bulk of the threats are from other countries.”
A 2012 cybersecurity study from NASCIO and Deloitte found half of U.S. states have just one to five full-time cybersecurity personnel.
Attackers’ current emphasis on cyber espionage may lead the U.S. government to redefine critical infrastructure. Traditionally, the term encompasses things like power grids, communications systems, finance, and transportation. However, last month President Obama signed an executive order giving the Secretary of Homeland Security until mid-July to extend the definition of critical infrastructure to include organizations “where a cybersecurity incident could reasonably result in catastrophic regional or national effects.” The list won’t include Netflix – consumer information technology services are specifically ineligible – but could conceivably include backbone Internet and cloud operators.
“You can rent a botnet for very little that can cause major disruption,” Mr. Cilluffo told the House subcommittee. “That’s not the same as destruction, but it can have a huge impact on companies that live and breath on just-in-time inventories and the ability to connect with their customers immediately.”
At what point do commercial operations become critical infrastructure, so far as the United States government is concerned?
“Five years ago, the definition of critical infrastructure was different, and it will continue to evolve,” noted Mr. Keanini. “In fact, that’s happening at a good rate.”
From state to street
The money and resources national governments can dedicate to cyber attacks can make them formidable. Sophisticated, highly-modular malware like Flame isn’t produced by a lone hacker pulling in a few all-nighters, but almost certainly represents skills and sustained efforts of well-compensated professional programmers – or at least a big bankroll and a willingness to ply the black market for exploits.
However, like other digital content, malware doesn’t stay contained. Exploits and techniques developed by state-sponsored efforts can be leaked or reverse-engineered just like any other malware, making their way into the hands of traditional cybercriminals and widely-available exploit collections like Blackhole, Phoenix, and RedKit.
“We have seen how vulnerabilities and techniques seen in complex threats (likely to be state-sponsored) have been used in other cyber crime activities,” noted Mr. Blasco. “They can be easily included in commercial exploit kits and used to install malware, steal banking credentials, or perform other activities.”
The terms “hacker,” “cybercriminal,” and “state-sponsored cyberattacker” could be distinctions without differences. A group calling itself Qassam Cyber Fighters claimed responsibility for attacks on U.S. banks last year, and they walk and talk more like Anonymous or the Occupy movement than an anti-American force. However, some security experts analyzing the attacks believe they must have help from other sources, and Senator Joseph Lieberman has said he believes they’re sponsored by Iran’s government. Cyber attacks during the brief Russia-Georgia war appear to have been conducted by individuals or criminal gangs with assistance from the Russian government; something similar may have occurred during cyber attacks on Estonia in 2007. Engaging hacker groups or online criminals to assist with cyber attacks could give nations a way to deny responsibility; however, it could also mean hackers and cybercriminals may have access to the state’s technical and fiscal resources.
Of course, state affiliations with hackers and cybercriminals could also be a smokescreen.
“In the tradecraft, nobody who’s good ever makes the news,” noted Mr. Keanini. “China always makes the news and is always getting caught, and one way to look at that is that they’re second-string or even third-string. Another way is that maybe some of it’s intentional.”
Duck and cover?
Despite the United States characterizing cyber threats as its biggest global risk– even above terrorism – it seems unlikely a single catastrophic cyber event like a “digital 9-11” looms on the immediate horizon. State attackers don’t seem to be ready or willing, and would-be attackers who are undoubtedly willing (e.g., traditional terror networks) currently lack the resources and expertise.
However, the digital landscape shifts quickly, and it’s certain that online attacks will become more sophisticated, particularly as more state-funded methods migrate to actors like cybercriminals and “hacktivists.”
Almost everyone involved in digital security agrees increased communication between governments and the private sector will be crucial to mitigating online attacks.
“Intelligence should be published in an automated, machine-consumable, standardized manner,” wrote Mandiant chief security officer Richard Bejtlich in a statement to the House Subcommittee on Cybersecurity, Infrastructure Protection, and Security Technologies. “Current systems rely on exchanging emails with documents that people must read and transcribe.”
“Collaboration is the key,” noted Mr. Blasco. “Most of the security capabilities available in the market are built by the private sector. Governments must help security companies to improve their products using some of the threat intelligence they collect.”


