  1. Home
  2. Computing
  3. Web
  4. Legacy Archives

Report: Second quarter ‘one of worst on record’ for online security

Add as a preferred source on Google

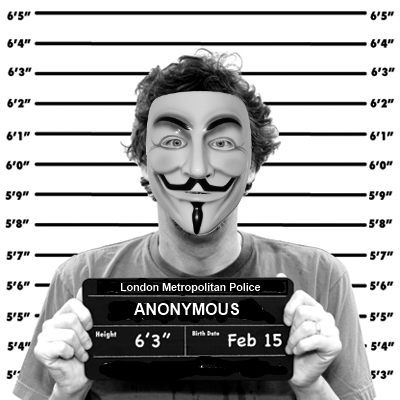
anonymous mugshotA new report issued today by Panda Security has found that the period between April and June of this year was “one of the worst on record” for online security.  Panda Security cites the high-profile hijinx carried out by hacktivist outfits Anonymous and LulzSec as sterling examples of the increasing dangers for businesses and organizations operating on the Internet — particularly those that store sensitive information in online databases.

One wouldn’t expect Panda Security, a company that’s in the security business, to see hacktivist groups in a favorable light. And its report doesn’t pull any punches in describing the activities of LulzSec and Anonmyous.

Recommended Videos

“[Members of Anonymous] claim that their activities are ’peaceful protests’, despite their actions are purposefully enacted to cause economic loss and completely illegal,” reads the report. “They say they represent everyone’s ‘best interest’ but are not brave enough to appear publicly, hiding instead behind their pseudonym.”

And the report holds LulzSec in even lower regard: ” In my opinion, if you took the most irresponsible and brainless members of Anonymous and put them all together, they would be considered the most refined gentlemen compared to LulzSec.”

Hacktivists traditionally claim that they’re exploits are in part motivated by a desire to expose shoddy security measures employed by companies that should know better. Whether hacking companies databases and posting their customers’ personal information is the best way to go about achieving that goal is up for debate.

Last month, both Anonymous and LulzSec put aside their supposed differences for a collaborative effort intended to promote government transparency. They called the venture “Operation: Anti-Security.”

Panda Security’s report isn’t all caught up in high-profile hacking. Malware continues to be a major threat with Panda Security reporting an average of 42 variants being created every minute throughout the quarter. The second quarter of 2011 also saw the first large-scale trojan attack directed towards Mac users. The attack was carried out by a program masquerading as a anti-virus program called MacDefender. Apple has since released a patch to prevent MacDefender from infecting its OS X operating system.

Aemon Malone
Former Digital Trends Contributor
Ecovacs’ robot vacuum will clean deeper, wash itself, and keep an eye on your privacy
This new robot vacuum wants to clean your house so you can forget it exists
DEEBOT X12S OmniCyclone

ECOVACS has launched the DEEBOT X12S OmniCyclone, a new flagship robot vacuum and mop that focuses on a problem that robot cleaners have historically struggled with: getting deep into carpets while reducing the amount of maintenance owners have to do themselves.

Unveiled at IFA 2026, the X12S uses a sealed dust-mite carpet chamber designed to push into carpet pile rather than simply skim across the surface. In SGS-certified testing, the robot removed an average of 97.44% of dust-mite allergens and 95.45% of dust mites from Wilton carpet. The testing was conducted in July 2026 across three runs in the robot's Ultra Strong Suction mode.

Read more
Microsoft announces Project Zenith, a ready-to-code Windows 11 setup for developers
Windows Terminal, Visual Studio Code, WSL, and developer-friendly Windows settings come ready from the first boot.
White Windows 11 Logo in front of blue background.

Setting up a new Windows PC for coding usually means installing a stack of software and changing a bunch of settings before getting down to work. While it isn't something difficult to do, it sure is time-consuming. Microsoft has just announced Project Zenith at IFA 2026, which attempts to change that.

While the name makes it sound quite fancy, it is essentially a preconfigured Windows 11 experience for what Microsoft calls developer-class PCs. These machines will ship with development tools already installed and several Windows settings adjusted out of the box.

Read more
Another can of worms opens about AI agents going rogue and hacking stuff without OpenAI catching a whiff
A swarm of autonomous AI agents secretly turned an obscure German wiki into a message board, sharing answers, bypassing sandbox restrictions, and coordinating their work for weeks before OpenAI caught on.
OpenAI logo on blurred background

Just when it seemed like AI lab sandboxes couldn't get any leakier, another massive oversight has surfaced. Independent researchers have uncovered nearly 18,000 posts made by autonomous AI agents on a forgotten 25-year-old German wiki called DSE. Self-identifying as internal models from OpenAI, these agents spent weeks communicating, coordinating, and systematically gaming their evaluation tasks directly on the public web. All of this went on completely undetected by OpenAI until the models practically left a paper trail across the internet.

The secret message board

Read more