  1. Home
  2. Computing
  3. Legacy Archives

Just reading about the China cybersecurity scare can get you hacked – here’s how

Add as a preferred source on Google
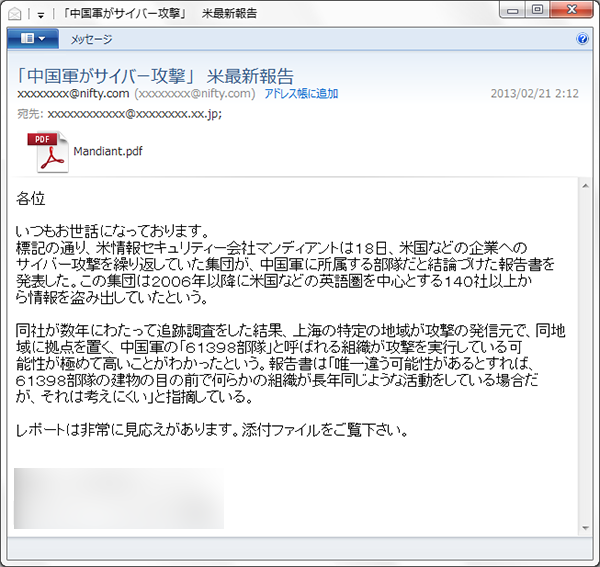
mandiant email attack
Image used with permission by copyright holder

China’s hacking the United States, according to an expose from Mandiant, which blew open the doors and tracked a network of hackers’ activities down to the very building. The report is an intriguing and straightforward read with few terms laymen would have to look up in a dictionary. If you’re trying to find the source of the report, here it is straight from Mandiant’s website. Otherwise do not, and we can’t stress this enough, do not open up suspicious emails.

There have been reports of phishing popping up in the news recently, what with Twitter, Pinterest, and Tumblr user’s email addresses . Phishing is an age old tactic since the dawn of email, but hackers have been getting increasingly clever with their tactics. Hackers don’t always need to be computer whizzes. Social engineers, who use social duping tactics, can use the right phrasing to sound like a legitimate entity, only to steal your information. Using both hacking skills and these social duping methods, someone is reportedly circulating a false Mandiant report that’s dropping Trojans onto victims’ computers.

Recommended Videos

Symantec says that the email sender claims to be from the press, who is recommending users to read the attached report. And by the looks of it, the report appears legitimate from a glance, thumbnail and all. The language of the email, based on the screen shot that Symantec displays, is in Japanese, and notes that the email may be sent in various languages. But here are a couple of pointers to ID the suspect email that Symantec points out: “Like in many targeted attacks, the email is sent from a free email account and the content of the email uses subpar language. It is obvious to a typical Japanese person reading the email that it was not written by a native speaker.”

Surprise, surprise, the delivery platform this hacker has decided to use is Adobe. When the victim opens up the attached PDF in the email, their computer is immediately infected. “The PDF file may drop Trojan.Swaylib and Trojan.Dropper, which drops Downloader,” Symantec researcher Joji Hamada writes. In some instances the Trojan masquerading as a PDF will drop malware.

Does this situation ring a bell? Just two weeks ago, Adobe had a zero-day exploit on their hands that would drop two DLLs (dynamic link library) onto the victim’s computer and would trick the computer into running malware. Well Adobe claimed to have patched that issue up, but with all of Adobe’s faults with Acrobat and Reader, it isn’t shocking that another vulnerability is being exploited. 

Francis Bea
Former Digital Trends Contributor
Francis got his first taste of the tech industry in a failed attempt at a startup during his time as a student at the…
Getting health advice from AI chatbots comes with a problem doctors may never see
Researchers say AI companies should face the same liability as doctors for bad health advice
ChatGPT and pills on the same canvas.

AI chatbots have quietly become a go-to source for medical advice the extent that some are dangerously skipping real doctors. But when AI's health advice goes wrong, doctors may never see the exchange behind it.

Researchers from Binghamton University, Stanford, Texas A&M, and Indiana University published a paper in Nature Health examining what happens after a chatbot gives you bad health information. Their biggest concern is not just that chatbots can be wrong. It is that those mistakes often leave no trace for doctors, researchers, or regulators to catch.

Read more
AI companies expect a catastrophic AI incident and are reportedly preparing for the aftermath
A major AI cyberattack could disrupt essential services, damage public trust, and spark a political fight over regulations.
openai-anthropic-logo-on-screen

Leaders at OpenAI, Anthropic, and other AI companies are reportedly preparing for a potential AI disaster that could turn the public against artificial intelligence. According to an Axios report, industry leaders are privately running through possible scenarios for what happens after a catastrophic AI incident.

What kind of AI disaster are companies preparing for?

Read more
Elon Musk’s SpaceX just made a big move to become a mobile carrier heavyweight in the US
SpaceX moves closer to becoming a major US mobile carrier with $8 billion deal
spacex

Elon Musk’s SpaceX is moving past satellite internet, and it’s making a big move into the US wireless market. The company has agreed to buy cellular spectrum licences from investment firm Grain Management in a deal reportedly worth about $8 billion, its biggest move yet to compete with established mobile carriers such as AT&T, Verizon and T-Mobile, according to a WSJ report.

The deal is for spectrum in the 800MHz band, which is for mobile services delivered via terrestrial infrastructure such as cell towers, not satellites. If the acquisition is approved, SpaceX could combine those airwaves with its growing Starlink satellite network to create a more comprehensive wireless service.

Read more